Why Did Hackers Raise French Supermarket Freezers to 50°C in Recent Cyber Intrusions?
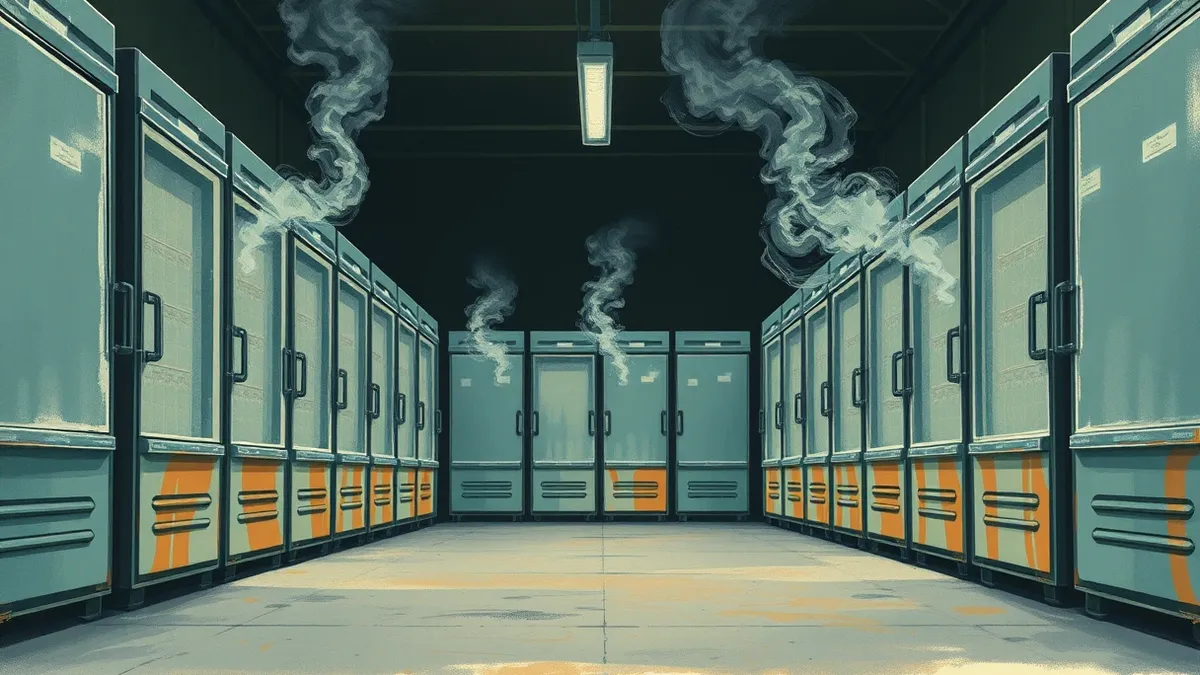
Cyber attackers manipulated refrigeration controls in France and the Netherlands, causing food spoilage by heating units to unsafe temperatures of 50°C.
Key points
- Hackers reportedly heated supermarket fridges to 50°C in France, spoiling food stocks.
- Stores in the Netherlands were also impacted by this cyber intrusion event.
- No specific vulnerability details or patch information have been released yet.
Cyber attackers successfully manipulated industrial refrigeration controls in French supermarkets, raising internal temperatures to 50°C according to reports from Hackread. This deliberate heating caused significant food spoilage within the affected stores. The incident highlights the physical risks posed by cyber intrusions targeting critical retail infrastructure components that manage temperature-sensitive goods.
Root cause
The exact technical vulnerability that allowed attackers to gain control over the refrigeration systems remains unclear. Hackread reports that hackers reportedly heated the units, but does not specify the software bug or configuration error that enabled this access. Without detailed technical disclosure, the specific root cause cannot be determined from current public information.
Attack path
Attackers gained unauthorized access to the systems controlling the supermarket freezers and fridges. They then manipulated these controls to raise the temperature to 50°C. This action directly resulted in the spoilage of food stocks stored within the affected retail locations in France. The attack path involved compromising the operational technology responsible for maintaining cold storage conditions.
Affected versions
No specific software versions or vendor products have been identified in the available reports. Hackread does not name the refrigeration system manufacturer or the specific firmware versions affected by this intrusion. Consequently, it is impossible to determine which equipment configurations are vulnerable based on the current source material.
Mitigation
No official fix, patch, or security update has been confirmed by any vendor for this incident. Organizations relying on industrial refrigeration systems should monitor vendor communications for any emerging advisories. Until specific vulnerabilities are disclosed, general cybersecurity hygiene and network segmentation remain the primary defensive measures for operational technology environments.
What to do and how to stay safe: cyberattack
- Monitor vendor security advisories for announcements regarding refrigeration system vulnerabilities.
- Ensure operational technology networks are segmented from corporate IT networks to limit lateral movement.
- Implement strict access controls and multi-factor authentication for systems managing physical infrastructure.
- Review logs for unusual changes in temperature settings or unauthorized configuration modifications.
General security guidance from the CloudSec Press newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
Which countries were affected by this cyberattack on supermarket refrigeration?
The cyberattack affected stores in France and the Netherlands, according to reports from Hackread.
What was the temperature set to during the attack?
Hackers reportedly heated the supermarket fridges to 50°C, causing significant food spoilage.
Has a patch been released for this vulnerability?
No patch or fix has been confirmed yet, as no specific vulnerability details have been disclosed.